The right move for most WordPress sites is to run Cloudflare with its official WordPress plugin, and enable Automatic Platform Optimization (APO) when your plan supports it. That combination gets you edge HTML caching, automatic cache purges on updates, free SSL, and a Web Application Firewall (WAF), without touching complicated server configs. The install takes about fifteen minutes. The section below walks through exactly how to do it.
TL;DR:
- Enabling Automatic Platform Optimization ensures full HTML caching at the edge, significantly reducing origin server trips for faster load times.
- The Cloudflare plugin must be configured correctly, including DNS confirmation, API token setup, and APO toggling, to avoid caching conflicts or setup failures.
- Setting SSL mode to “Full” or “Full (Strict)” and enabling features like Always Use HTTPS and Automatic HTTPS Rewrites is crucial for secure, error-free operation.
- APO does not support multisite setups, so site owners with networked WordPress sites should plan accordingly before activation.
- Regularly checking the
cf-edge-cacheresponse header verifies whether edge caching is active and prevents delays or caching conflicts.
Table of Contents
- What Does Cloudflare Do for WordPress?
- How Do You Install and Activate the Cloudflare Plugin?
- Which Cloudflare Dashboard Settings Matter Most for WordPress?
- How Do You Activate and Verify APO?
- Why Does Cloudflare Sometimes Conflict With Other Plugins?
- What Security Settings Should WordPress Sites Enable on Cloudflare?
- What Does an Agency-Level Cloudflare Setup Actually Look Like?
- When Does Cloudflare Plus APO Actually Pay Off?
- Get Cloudflare Set Up Right the First Time
- Where to Verify These Settings Yourself
- Sources
- FAQ
What Does Cloudflare Do for WordPress?
The Cloudflare WordPress plugin is what separates a good Cloudflare setup from a mediocre one. It applies Cloudflare’s recommended settings automatically and, just as important, purges the cache the moment you publish or update content. Without the plugin, you’re stuck manually clearing cache every time you edit a post, which most site owners forget to do until a client complains a page “looks old.”
APO is the other half of the story, and it’s the part most guides skip. A standard CDN only caches static files like images and CSS. APO caches the full dynamic HTML page at Cloudflare’s edge, which is a different mechanism entirely, and it’s why APO sites often see meaningfully better Time to First Byte and First Contentful Paint scores.
Here’s what that combination delivers in practice:
- One-click application of Cloudflare’s recommended WordPress settings
- Automatic cache purge tied to post publishing and updates
- Free SSL certificates and WAF rules out of the box
- Edge HTML caching through APO, cutting origin server trips
One catch worth flagging early: APO does not currently support multisite installations, so if you’re running a network of sites, plan around that before you commit.
How Do You Install and Activate the Cloudflare Plugin?
Getting Cloudflare running on WordPress involves two systems talking to each other: your DNS and your plugin settings. Here’s the order that avoids downtime.
- Create a free Cloudflare account and add your domain. Cloudflare scans your existing DNS records automatically.
- Confirm every DNS record imported correctly before moving forward. Missing a record here is the single most common cause of “my site broke when I set up Cloudflare.”
- Update your nameservers at your domain registrar to the two Cloudflare nameservers shown in your dashboard. Propagation can take anywhere from a few minutes to 24 hours.
- Install the Cloudflare plugin from the WordPress.org plugin directory, or upload the ZIP file manually, then activate it.
- Generate a WordPress API token inside your Cloudflare account and paste it into the plugin’s settings screen to link the two.
- Click “Apply Default Settings” inside the plugin, then toggle on APO if your plan supports it.
Pro Tip: Do this on a staging copy of your site first if you’re managing a live business site. Nameserver changes and cache settings are low risk, but testing on staging means zero chance of a surprise outage during business hours.
Once it’s live, check your site’s response headers for cf-edge-cache. If it reads cache,platform=wordpress, the plugin and APO are both working correctly.
Which Cloudflare Dashboard Settings Matter Most for WordPress?
The plugin handles the basics, but a few dashboard settings deserve a manual check, especially if you inherited a Cloudflare account someone else configured years ago.
Start with SSL/TLS. Set the mode to “Full” or “Full (Strict)” if your origin server already has an SSL certificate, which most hosts provide free now. Avoid “Flexible” mode: it encrypts traffic between the visitor and Cloudflare but leaves the connection from Cloudflare to your server unencrypted, which defeats half the purpose of SSL.
From there:
- Turn on Always Use HTTPS and Automatic HTTPS Rewrites to catch mixed-content warnings automatically
- Set Bypass Cache on Cookie so logged-in visitors always see fresh content instead of a cached page meant for anonymous traffic
- Skip Cache Everything if APO is active. It’s already handling HTML; stacking both can cause conflicting cache rules
- Enable Polish for automatic image compression and confirm HTTP/2 is active, both usually on by default
- Use Page Rules to exclude
/wp-admin, login pages, and cart pages from aggressive caching
One setting worth extra caution: Rocket Loader. It defers JavaScript loading for speed, but it breaks interactive elements on some page builders and themes. Test it on staging before flipping it on for a live site.
Cloudflare’s own performance documentation notes that Bypass Cache on Cookie is what allows anonymous pages to be fully cached while preserving dynamic behavior for logged-in users, which is the setting most WordPress admins overlook entirely.
How Do You Activate and Verify APO?
APO won’t turn on correctly if you skip a prerequisite, so check these four items first: nameservers pointed to Cloudflare, DNS confirmed, the plugin installed and active, and your API token connected. Cloudflare’s own get-started documentation lists this exact order for a reason. Skipping the DNS confirmation step is the most common reason APO “doesn’t work” for people.
- Open the Cloudflare plugin settings in WordPress and locate the APO toggle
- Enable it. If your account is on the free plan, APO is an add-on with its own monthly cost; some paid Cloudflare plans include it
- Confirm your setup isn’t a multisite install, since APO doesn’t support that configuration yet
- Reload your homepage and inspect the response headers for
cf-edge-cache
Here’s what to look for once it’s live:
| Check | What you’re looking for | What it means |
|---|---|---|
| Response header | cf-edge-cache: cache,platform=wordpress |
APO is actively caching HTML at the edge |
| Time to First Byte | Noticeably lower than before activation | Origin server trips are being reduced |
| Cache purge test | Header updates within seconds of publishing | Automatic purge is functioning |
If the header never appears, double check the nameservers propagated fully. That’s the most common blocker.
Why Does Cloudflare Sometimes Conflict With Other Plugins?
Cloudflare doesn’t play well with every caching setup, and the fix usually isn’t complicated once you know where to look. Plugins like WP Rocket or W3 Total Cache manage caching at the server level, and running them alongside APO can create two competing cache layers that serve stale versions of the same page.
- Disable one caching layer at a time and reload the page to isolate which one is causing the stale content
- After any content update, manually purge the Cloudflare cache from the dashboard if the automatic purge doesn’t fire
- Check the
cf-edge-cacheheader again after purging to confirm the new version is actually being served - If your host runs Varnish in front of WordPress, you may be dealing with three cache layers rather than two, which is where things get genuinely messy
Page builders sometimes complicate this further. This breakdown of caching plugin behavior with popular builders is worth a look if you’re troubleshooting a site built on Elementor or a similar tool.
Pro Tip: If you’re three cache layers deep and still seeing stale content after 20 minutes of troubleshooting, that’s the point to call in help rather than keep guessing. Multisite and Varnish stacks are where DIY troubleshooting stops being worth the hours.
What Security Settings Should WordPress Sites Enable on Cloudflare?
Cloudflare’s free plan covers the basics, but WordPress sites benefit from a few settings that go beyond default protection.
- Enable WordPress-specific WAF rulesets if you’re on a paid plan; they’re tuned to block common WordPress exploit patterns like XML-RPC abuse and login brute-forcing
- Turn on rate limiting or Cloudflare’s “I’m Under Attack” mode temporarily if you notice a traffic spike that looks like a bot attack
- Stick with Full or Full (Strict) SSL/TLS mode, never Flexible, and keep Always Use HTTPS on to close mixed-content gaps
- Test your site immediately after enabling any WAF rule, since overly aggressive rules occasionally block legitimate form submissions or login attempts
- Keep WordPress core, plugins, and PHP versions current. Cloudflare protects the perimeter, but an outdated plugin is still an open door
None of these settings replace basic WordPress hygiene. They add a layer in front of it.
What Does an Agency-Level Cloudflare Setup Actually Look Like?
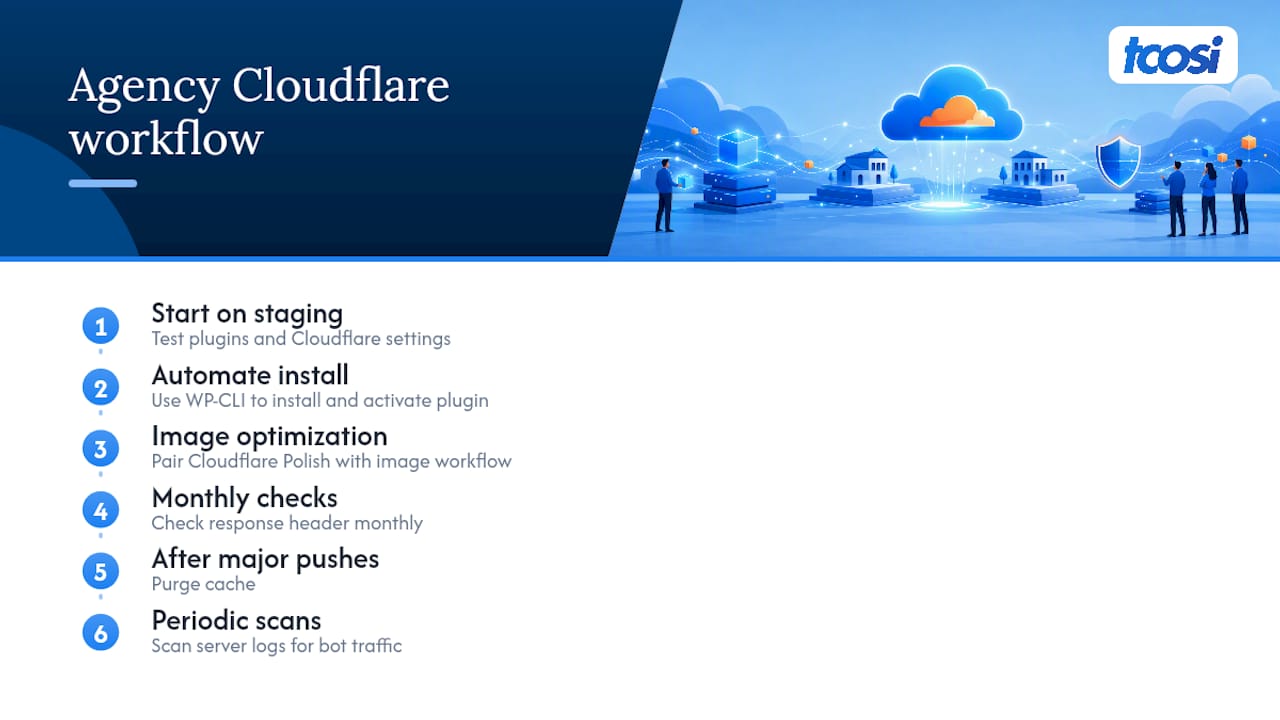
The pattern we follow on client sites starts with staging, not production. Every plugin install and every Cloudflare setting gets tested on a staging environment first, because a nameserver change that goes sideways on a live client site is a much worse afternoon than the same mistake on staging.
For repeatable work across multiple sites, WP-CLI beats clicking through the dashboard every time. It installs and activates the Cloudflare plugin with one command, which matters when you’re managing more than a handful of sites.
Pairing Cloudflare’s Polish setting with a proper image optimization workflow cuts origin bandwidth further than Polish alone. Routine maintenance means checking the cf-edge-cache header monthly, purging cache after major content pushes, and scanning server logs occasionally for bot traffic that’s slipping past the CDN layer unnoticed.
When Does Cloudflare Plus APO Actually Pay Off?
Cloudflare and APO deliver the biggest return for small business sites running on modest shared or mid-tier hosting, where every millisecond shaved off Time to First Byte shows up directly in bounce rate. If your host already includes a strong server-side cache and a CDN, the marginal gain shrinks.
The trade-offs are real: APO carries its own cost on the free plan, multisite is off the table entirely, and stacking Cloudflare with another caching plugin invites conflicts if nobody’s watching. My honest advice is to set a monthly reminder to check that cf-edge-cache header and your core web vitals. The moment you’re troubleshooting cache conflicts for the third time in a month, that’s your signal to bring in someone who does this daily rather than keep experimenting on a live site.
— Tommy Cosimano
Get Cloudflare Set Up Right the First Time
You can get a staging-first install, WP-CLI deployment, APO activation done correctly the first time, image optimization tuned to work with Cloudflare’s Polish setting, and ongoing maintenance so nobody has to remember to purge a cache after every update.

A typical engagement starts with a quick audit of your current setup: DNS, SSL mode, plugin conflicts, and whether APO even makes sense for your hosting situation. From there, the install is handled and you get a site that’s faster and easier to maintain. For information about ongoing plugin and security management, see the website pricing page for details on what’s included at each tier.
Where to Verify These Settings Yourself
The Cloudflare WordPress plugin page covers current features and changelog history for compatibility checks. Cloudflare’s own APO get-started guide walks through prerequisites in more depth, and its performance support docs cover image and caching specifics not included here.
Sources
FAQ
Can I Use Cloudflare With WordPress?
Yes. Cloudflare works with any WordPress site regardless of host, and the official plugin is built specifically to apply WordPress-recommended settings automatically.
What Are the Downsides of Using Cloudflare?
The main risks are cache conflicts with other caching plugins, a learning curve around DNS and nameserver changes, and APO’s lack of multisite support. Most of these are avoidable by testing changes on staging first.
Is Cloudflare Free for Domains?
Cloudflare’s core CDN, SSL, and basic WAF protection are free. Some features, including APO on the free plan, carry an added monthly cost.
Is Cloudflare a Good Domain Registrar?
Cloudflare does offer domain registration at cost with no markup, but most WordPress site owners use Cloudflare for its CDN, security, and caching features rather than as their registrar.
How Do I Know If APO Is Actually Working?
Check your site’s response headers for cf-edge-cache: cache,platform=wordpress. If that value appears, edge HTML caching is active.